On March 16, I blogged about how Ernest & Young had lost a laptop containing the social security numbers and other personal information to its clients employees. Then we found out that IBM, HP and Cisco employees were also affected.
Well the plot thickens. The Register is reporting that Ernst & Young lost information on 243,000 Hotels.com customers as well. Is it the same laptop? No one knows at this point, but I am leaning toward that idea.
Friday, June 2, 2006


Mozilla Firefox and Thunderbird 1.5.0.4 Released
Get'em while their hot.
Secunia has the details on the critical vulnerabilities released for both Firefox and Thunderbird.
Mozilla has released 1.5.0.4 to counter these vulnerabilities.
Secunia has the details on the critical vulnerabilities released for both Firefox and Thunderbird.
Mozilla has released 1.5.0.4 to counter these vulnerabilities.
Thursday, June 1, 2006
Tools of the Trade - New and Updated
Lets have a look some of the new and updated tools out in the field:
1) Yesterday the Openwall Project released John the Ripper Pro. It is currently available for Linux on x86 processors, with support for the latest Intel and AMD process features such as SSE2.
The features currently specific to the Pro versions are:
1) Yesterday the Openwall Project released John the Ripper Pro. It is currently available for Linux on x86 processors, with support for the latest Intel and AMD process features such as SSE2.
The features currently specific to the Pro versions are:
- Pre-built and well-tested native package (RPM) which may be installed with a single command - no need to compile
- Automatic detection of processor architecture extensions such as SSE2 and MMX for much faster processing, with transparent fallback on older CPUs
- A large multilingual wordlist optimized specifically for use with John the Ripper (4,106,923 entries, 43 MB uncompressed) is included in the package, and John the Ripper is pre-configured for its use
- The included documentation is revised to be specific for the given package and OS rather than generic, making it easier to understand
As a bonus, the full source code sufficient to rebuild the package is also provided (can be downloaded separately)
2) On May 23th, Metasploit v2.6 was released. This relese includes 43 more exploits, numerous bug fixes, improvements to the SMB/DCERPC layers and a few cosmetic changes.
3) On May 22th, Cain & Abel v2.9 was released.
New features include:
- Added Ophcrack's RainbowTables support for LM Hashes Cryptanalysis attack.
- Added hashes syncronization functions (Export/Import) to/from Cain for PocketPC via ActiveSync.
- Added VoIP sniffer support for the following codecs: G723.1, G726-16, G726-24, G726-32, G726-40, LPC-10.
- Added support for Winpcap v3.2.
4) Paros Attack Proxy has been updated to v3.2.12.
New Features include:
- Use newest external library for HTTP handling.
- enable/disable spider to POST forms in options panel to avoid generating unwanted traffic (default to enable). This is requested by many users.
- Decrease the number of possible combinations crawled by spider on forms with multiple SELECT/OPTIONS. This make crawling less resource consuming and lower chance to affect application being scanned.
- Minor UI changes.
Fixes include:
- Fallback database library to previous version as in Paros 3.2.10 because of a problem with hsqldb where some byte combination may consume 100% cpu time.
- Increase width of method display in history to cater for other longer method names.
- Default file scans may display incorrect HTTP message body if the original message is a POST request.
5) FileZilla 2.2.24a was released recently.
Personal Data of 1.3 million Borrowers Lost
Via the Austin Statesman.com -
Texas Guaranteed Student Loan Corp. said a contractor has lost a piece of equipment containing the names and Social Security numbers of 1.3 million borrowers.
But there is no evidence, the company stressed Wednesday, that the information has been misused.
The loss occurred May 24, but Texas Guaranteed didn't find out about it until Friday. It then spent the Memorial Day weekend identifying whose information was on the missing equipment. "It was not a security breach where someone hacked into our system," said Sue McMillin, Texas Guaranteed's president and chief executive. "At this point, we are not aware of any impact."
Round Rock-based Texas Guaranteed said it had sent encrypted electronic files containing the names and Social Security numbers to an office for Toronto-based Hummingbird Ltd., which helps companies manage large amounts of information. No other personal information was sent, Texas Guaranteed officials said.
A Hummingbird employee downloaded, decrypted and stored the files on a piece of equipment that was later lost. The companies declined to elaborate on what the equipment was, where it was lost or what specific law-enforcement authorities were notified other than to say it was local police in a U.S. city.
"I don't want to give out any information that could make it easier for anybody to do anything," Hummingbird President and chief executive Barry Litwin said. But, he added, it is "extremely unlikely" for the information to be used inappropriately because it is password-protected "many times over."
So the data is not encrypted but password protected? By what? The Windows XP login password? I love how the media always stresses how the information hasn't been used in bad way, instead of talking about what they are going to do to prevent it in the future. It doesn't make me feel comfortable to hear, "At this point, we are not aware of any impact."
Wait, I am aware of a couple impacts.
1) You lost the personal information on over million people.
2) Smart ID crooks are just going to wait 6 months before using the information. By this time you aren't watching and the customer is no longer watching. So saying that there is no bad activity at this point is just silly.
I will agree that most lost laptop cases do not result in massive ID crimes. Perhaps the thief just wants the quick money for the physical equipment. If this has been the case up to now, then we should call it luck.
Because real crooks with serious information security understanding can pull off a grab job like this in their sleep and then eat your account dry before you know what hit you.
Texas Guaranteed Student Loan Corp. said a contractor has lost a piece of equipment containing the names and Social Security numbers of 1.3 million borrowers.
But there is no evidence, the company stressed Wednesday, that the information has been misused.
The loss occurred May 24, but Texas Guaranteed didn't find out about it until Friday. It then spent the Memorial Day weekend identifying whose information was on the missing equipment. "It was not a security breach where someone hacked into our system," said Sue McMillin, Texas Guaranteed's president and chief executive. "At this point, we are not aware of any impact."
Round Rock-based Texas Guaranteed said it had sent encrypted electronic files containing the names and Social Security numbers to an office for Toronto-based Hummingbird Ltd., which helps companies manage large amounts of information. No other personal information was sent, Texas Guaranteed officials said.
A Hummingbird employee downloaded, decrypted and stored the files on a piece of equipment that was later lost. The companies declined to elaborate on what the equipment was, where it was lost or what specific law-enforcement authorities were notified other than to say it was local police in a U.S. city.
"I don't want to give out any information that could make it easier for anybody to do anything," Hummingbird President and chief executive Barry Litwin said. But, he added, it is "extremely unlikely" for the information to be used inappropriately because it is password-protected "many times over."
So the data is not encrypted but password protected? By what? The Windows XP login password? I love how the media always stresses how the information hasn't been used in bad way, instead of talking about what they are going to do to prevent it in the future. It doesn't make me feel comfortable to hear, "At this point, we are not aware of any impact."
Wait, I am aware of a couple impacts.
1) You lost the personal information on over million people.
2) Smart ID crooks are just going to wait 6 months before using the information. By this time you aren't watching and the customer is no longer watching. So saying that there is no bad activity at this point is just silly.
I will agree that most lost laptop cases do not result in massive ID crimes. Perhaps the thief just wants the quick money for the physical equipment. If this has been the case up to now, then we should call it luck.
Because real crooks with serious information security understanding can pull off a grab job like this in their sleep and then eat your account dry before you know what hit you.
Wednesday, May 31, 2006
Swedish Government Shuts Down "The Pirate Bay"
Via Thepiratebay.org -
In the morning of 2006-05-31 the Swedish National Criminal Police showed a search warrant to RixPort80 personnell. The warrant was valid for all datacentres of RixPort80 and was directed at The Pirate Bay. The allegation was breach of copy-right law, alternatively assisting breach of copy-right law.
I suppose it was only a matter of time.....
In the morning of 2006-05-31 the Swedish National Criminal Police showed a search warrant to RixPort80 personnell. The warrant was valid for all datacentres of RixPort80 and was directed at The Pirate Bay. The allegation was breach of copy-right law, alternatively assisting breach of copy-right law.
I suppose it was only a matter of time.....
Stardust: OpenOffice PoC Virus
A new PoC virus has been developed that targets OpenOffice and StarOffice only.
Check this SF article for more details.
An unknown virus writer has created the first macro virus that targets computers running the alternative word processors OpenOffice and StarOffice, antivirus firm Kaspersky Labs said on Tuesday.
The virus, which Kaspersky called StarOffice.Stardust.A on its Viruslist blog, is written in StarBasic, a variant of the BASIC programming language designed for scripting common functions in the StarOffice and OpenOffice word processors. While the virus attempts to spread to computers through OpenOffice and StarOffice, Kaspersky called the functionality theoretical.
Check this SF article for more details.
An unknown virus writer has created the first macro virus that targets computers running the alternative word processors OpenOffice and StarOffice, antivirus firm Kaspersky Labs said on Tuesday.
The virus, which Kaspersky called StarOffice.Stardust.A on its Viruslist blog, is written in StarBasic, a variant of the BASIC programming language designed for scripting common functions in the StarOffice and OpenOffice word processors. While the virus attempts to spread to computers through OpenOffice and StarOffice, Kaspersky called the functionality theoretical.
Tuesday, May 30, 2006
Fun: Recently Unearthed E-Mail Reveals What Life Was Like In 1995
It was on theOnion.com, it has to be true.
Sunday, May 28, 2006
THC Courts Phone Hackers
On May 25th, The Hackers Choice (THC) released ROMs and memory mapping information for a nice group of Nokia mobile phones.
Posted on THC.org by DerSteppenwolf :
THC is the world's first group to release ROM images and memory maps from Nokia Mobile Phones. This is an invitation for Reverse Engineers and hackers to discover hidden secrets and backdoors on mobile phones.
http://thc.org/thc-rom/
Posted on THC.org by DerSteppenwolf :
THC is the world's first group to release ROM images and memory maps from Nokia Mobile Phones. This is an invitation for Reverse Engineers and hackers to discover hidden secrets and backdoors on mobile phones.
http://thc.org/thc-rom/
The Perfect Recipe for Defacement
It is that time of year. College is ending and summer is about to begin - the perfect recipe for defacement.
It appears that Turkey as a whole isn't letting up on the defacements. They can account for over half of all the defacements tracked by Zone-H.org - taking the spot from Brazil just recently.
Recent Turkish Defacements
aLpTurkTegin - http://woodlandsperfumers.com/
SanalYargic - http://grupocastor.com.uy/portal/index.php
TurkStorm.Org - http://www.progtv.be/
yusufislam - http://gladtidingsofduluth.org/forum/
narcotic - http://upload.neuper-team.com/index.html
The list goes on and on....
The Internet Storm Center is already reporting a possible "script kiddie contest" underway. Crazy kids.
Looks like alot of the defacements are caused by PHP security issues.
It appears that Turkey as a whole isn't letting up on the defacements. They can account for over half of all the defacements tracked by Zone-H.org - taking the spot from Brazil just recently.
Recent Turkish Defacements
aLpTurkTegin - http://woodlandsperfumers.com/
SanalYargic - http://grupocastor.com.uy/portal/index.php
TurkStorm.Org - http://www.progtv.be/
yusufislam - http://gladtidingsofduluth.org/forum/
narcotic - http://upload.neuper-team.com/index.html
The list goes on and on....
The Internet Storm Center is already reporting a possible "script kiddie contest" underway. Crazy kids.
Looks like alot of the defacements are caused by PHP security issues.
Saturday, May 27, 2006
BackTrack 1.0 Final Released
Remote-exploit.org has finally released BackTrack 1.0 Final.
If you are still using Security Auditor or WHAX, then catch up with the times and get the new BackTrack...you will be glad you did.
If you are still using Security Auditor or WHAX, then catch up with the times and get the new BackTrack...you will be glad you did.
Apple Failed in Battle to Slient the "Media"
Charles Cooper has a great article over at CNet.com -
Hopefully Apple is making an effort to find the leaks inside, instead of just pulling the A-team of lawyers out at the drop of a hat.
Friday, May 26, 2006
Microsoft Word Unspecified Remote Code Execution - UPDATED
I am a little late on this update, but I have been really busy this week. The exploit is a zero-day for sure.
Most of the antispyware friends that I talked to have samples and didn't really see anything different than has already been reported. But it did take a while for everyone to get a sample, this shows just how rare it is in the wild.
I have a sample as well, but haven't had a chance to look at it. I have almost zero RCE skills, so I don't think having a sample is going to help me understand it much better.
The first attack was very limited in scope and Microsoft appears to be doing the right think and will not jump the gun to release a patch early. Some people are giving them hell about that, but I don't see a real reason for them to rush it at this point - in this exact case.
In some cases, it doesn't make sense to hold the patch until Patch Tuesday.
If the vulnerable function is known and being exploited in the public, then the patch should be released as soon as it is ready. Releasing it early in this current case, will expose the true vulnerability to groups that may not have it now, and in the end this will only increase the number of active exploits against this vector.
SANS - http://isc.sans.org/diary.php?storyid=1345
Microsoft - http://www.microsoft.com/technet/security/advisory/919637.mspx
Most of the antispyware friends that I talked to have samples and didn't really see anything different than has already been reported. But it did take a while for everyone to get a sample, this shows just how rare it is in the wild.
I have a sample as well, but haven't had a chance to look at it. I have almost zero RCE skills, so I don't think having a sample is going to help me understand it much better.
The first attack was very limited in scope and Microsoft appears to be doing the right think and will not jump the gun to release a patch early. Some people are giving them hell about that, but I don't see a real reason for them to rush it at this point - in this exact case.
In some cases, it doesn't make sense to hold the patch until Patch Tuesday.
If the vulnerable function is known and being exploited in the public, then the patch should be released as soon as it is ready. Releasing it early in this current case, will expose the true vulnerability to groups that may not have it now, and in the end this will only increase the number of active exploits against this vector.
SANS - http://isc.sans.org/diary.php?storyid=1345
Microsoft - http://www.microsoft.com/technet/security/advisory/919637.mspx
Blah: Long Weekend
Well, I am on my way back from Washington DC. Been a crazy long week, I am ready to get home.
It is amazing the see how empty the Houston airport can be on a Friday night. All the shops are closed and my ice latte is all watered down now. I suppose it is time to break out the redbull and security books until my flight.
Everyone have a great holiday weekend and don't get into too much trouble.
For your weekend reading, check up on the new Norton Corporate Anti-virus hole discovered by eEye and read about this special ring-tone used by teenagers in class.
It is amazing the see how empty the Houston airport can be on a Friday night. All the shops are closed and my ice latte is all watered down now. I suppose it is time to break out the redbull and security books until my flight.
Everyone have a great holiday weekend and don't get into too much trouble.
For your weekend reading, check up on the new Norton Corporate Anti-virus hole discovered by eEye and read about this special ring-tone used by teenagers in class.
Wednesday, May 24, 2006
ScanDoo Beta - Making Searching Safe
I just found this pretty cool search engine today. It doesn't replace Google, it just makes it more safe for the public.
It is called ScanDoo.
Scandoo is based on ScanSafe’s web security technology that currently scans billions of web requests for corporate employees around the world. ScanSafe software developers were often asked by their friends and family if they could protect home Internet use in the same way that they protect corporate users. When our lab came up with safe searching technology we thought it was such a good idea that we wanted to make it available to all.
When you search in Scandoo, each site is compared to the ScanSafe's database and given an icon.
This is a great idea for those people that search at work...and don't want the proxy admin at their desk ;)
It is called ScanDoo.
Scandoo is based on ScanSafe’s web security technology that currently scans billions of web requests for corporate employees around the world. ScanSafe software developers were often asked by their friends and family if they could protect home Internet use in the same way that they protect corporate users. When our lab came up with safe searching technology we thought it was such a good idea that we wanted to make it available to all.
When you search in Scandoo, each site is compared to the ScanSafe's database and given an icon.
- Green Check is safe
- Yellow is a warning
- Red is bad
- Black Bug is totally unsafe - known website that contains malware or evil script
This is a great idea for those people that search at work...and don't want the proxy admin at their desk ;)
Tuesday, May 23, 2006
Veterans Affairs Department- data on millions of veterans stolen
Via GCN.com -
The Veterans Affairs Department today revealed that personal, identifying data for as many as 26 million American veterans was stolen from a VA employee's home in May. The information is a list of all veterans who served in the military and were discharged since 1975. A VA employee took files home as part of department work on a data collation project to simplify some VA processes. Subsequently, someone broke into the employee’s home and stole the data. The career employee, a data analyst, was not authorized to take the files home, said VA secretary Jim Nicholson in a teleconference with reporters. He would not say what form the data was in.
I am going to guess and say CSV. ;)
In light of this news, William Jackson wrote a pretty good little article over at GCN.com as well. It is just a reminder that we aren't just holding a PC in our hands, we are holding data that other people might want.
The Veterans Affairs Department today revealed that personal, identifying data for as many as 26 million American veterans was stolen from a VA employee's home in May. The information is a list of all veterans who served in the military and were discharged since 1975. A VA employee took files home as part of department work on a data collation project to simplify some VA processes. Subsequently, someone broke into the employee’s home and stole the data. The career employee, a data analyst, was not authorized to take the files home, said VA secretary Jim Nicholson in a teleconference with reporters. He would not say what form the data was in.
I am going to guess and say CSV. ;)
In light of this news, William Jackson wrote a pretty good little article over at GCN.com as well. It is just a reminder that we aren't just holding a PC in our hands, we are holding data that other people might want.
Sunday, May 21, 2006
Google Summer of Code 2006
It is almost that time again. On Tuesday (May 23th), the official projects will be released on the Google Summer of Code website.
While it is impossible to talk about all the possible projects, here are a couple of ideas from a couple of the project. Remember, these are just ideas. Students are welcome to submit original ideas and we will see some of those when the dust settles.
Apache SoC 2006
Mozilla SoC 2006
FreeBSD SoC 2006
My coding skillz are very very far from Kung Foo level, but I just might apply for this project idea suggested for Nmap SoC 2006:
------------------------
Slacker
Nmap developers are known as some of the most productive in the open source world. In order to crank out more code, many eschew luxuries like classes, social lives, sex, and sleep. To counterbalance all of this planned productivity, we may need some experienced slackers to spend the summer playing video games, watching TV, reading Slashdot, and dating. You will report these activities in a weekly status report so the rest of us can live our lives vicariously through yours.
Since lazyness is a virtue for this position, our normal application form is not required. Just tell us your best time-wasting story or any other relevant credentials for this critical role.
------------------------
In 2005, there were around 43 mentoring groups signed up for the Summer of Code.
This year they have over 100.
This fall, we should see a ton of great enchancements and new features created by the community for the community. Open source, it is a good thing....
While it is impossible to talk about all the possible projects, here are a couple of ideas from a couple of the project. Remember, these are just ideas. Students are welcome to submit original ideas and we will see some of those when the dust settles.
Apache SoC 2006
Mozilla SoC 2006
FreeBSD SoC 2006
My coding skillz are very very far from Kung Foo level, but I just might apply for this project idea suggested for Nmap SoC 2006:
------------------------
Slacker
Nmap developers are known as some of the most productive in the open source world. In order to crank out more code, many eschew luxuries like classes, social lives, sex, and sleep. To counterbalance all of this planned productivity, we may need some experienced slackers to spend the summer playing video games, watching TV, reading Slashdot, and dating. You will report these activities in a weekly status report so the rest of us can live our lives vicariously through yours.
Since lazyness is a virtue for this position, our normal application form is not required. Just tell us your best time-wasting story or any other relevant credentials for this critical role.
------------------------
In 2005, there were around 43 mentoring groups signed up for the Summer of Code.
This year they have over 100.
This fall, we should see a ton of great enchancements and new features created by the community for the community. Open source, it is a good thing....
Saturday, May 20, 2006
New Computer Laws - Are they too Broad?
Recently, several new bills here in the US and in the EU could have a pretty big impact on the IT security world. Are they too broad? Can we fix them before it is too late? Is it even possible to fix them?
There are hard questions and I don't have all the answer, but here are same of my thoughts on the issue.
There are hard questions and I don't have all the answer, but here are same of my thoughts on the issue.
1) Dual-Edged Sword - The tricks, skills and tools of the IT security world are commonly called dual-edged swords. Security tools are just that - tools, no different than a gun, a sword, a hammer or a butter knife. We deal with these pretty good in the real world. Cops don't go out into the woods and arrest hunters because they are carrying shotguns. Do they? Intent and context are the true factors that give the law weight. Exploits, like guns, can be used to break into a network...but that same exploit can be used by a security network admin to find a vulnerable server on the network and as a result jump start the protection process.
2) The Grey World - For a long time, I have talked with my friends about the balance of the force in the world. People have the ability to be good or bad, tools have the ability to be used for good or bad. The world truly is Yin and Yang. I am a huge believer in maintaining the balance. Most of the governments in the world are based on the idea and will fail to function without it. If the balance is not maintained, then things start to function in ways that are not desired - Absolute power corrupts absolutely.
So how do we as a world, apply the black & white letters of the law to a world of grey? Very carefully, that is how. It is like a never ending dance...ever changing, ever shaping. What is illegal today could be legal tomorrow...and vice vera. This idea seems very simple when applied to the real world...but it becomes much more cloudy when applied to the virtual world.
We are seeing just how cloudly with these new bills:
1) Possible Update to the UK Computer Misuse Act (CMA)
2) Truth in Caller ID Act of 2006 - this one is pretty good since this trick rarely needed beyond law enforcement....that assumes I am ok with PI's tricking people..umm...I guess so.
4) UK RIP Act - forcing people to hang over encryption keys....
So how do we make objective laws that take into account subjective intent and context? That is a question for the ages, I think.
Friday, May 19, 2006
Microsoft Word Unspecified Remote Code Execution
Several anti-virus companies have identified a new unspecified attack against Microsoft Word. It is currently being to drop a backdoor trojan onto the target. Once infected the computer attempts to connect to a server in China (localhost.3322.org).
Symantec has tagged the new backdoor as Backdoor.Ginwui. Norton detects the dropped trojan as Trojan.Mdropper.H - but this is expected to change in my view. This dropped trojan could be replaced in the future with a new altered trojan that is not detected.
Some people are using the term 0-day, but until more information is known, I don't want to use that.
Remember that Microsoft patched several Office remote code execution bugs in MS06-012.
Symantec has tagged the new backdoor as Backdoor.Ginwui. Norton detects the dropped trojan as Trojan.Mdropper.H - but this is expected to change in my view. This dropped trojan could be replaced in the future with a new altered trojan that is not detected.
Some people are using the term 0-day, but until more information is known, I don't want to use that.
Remember that Microsoft patched several Office remote code execution bugs in MS06-012.
Thursday, May 18, 2006
Fun: 48-Hour Internet Outage Plunges Nation Into Productivity
Via TheOnion.com -
BOSTON—An Internet worm that disabled networks across the U.S. Monday and Tuesday temporarily thrust the nation into its most severe maelstrom of productivity since 1992.
"In all my years, I've never seen anything like this," said Price Stern Sloan system administrator Andrew Walton, whose effort to restore web service to his company's network was repeatedly hampered by employees busily working at their computers. "The local-access network is functioning, so people can transfer work projects to one another, but there's no e-mail, no eBay, no flaminglips.com. It's pretty much every office worker's worst nightmare."
According to Samuel Kessler, senior director at Symantec, which makes the popular Norton Antivirus software, the Internet "basically collapsed" Monday at 8:34 a.m. EST.
The Gibe-F worm, an e-mail-transmittable virus, initiated cascading server failures. Within an hour, Internet service to more than 90 percent of the U.S. was disabled, either by the worm or by network firewalls that initiated security protocols.
"Unlike SoBig or Blaster, this worm didn't harm individual computers; it just used them as a gate to attack the Internet at the ISP level," Kessler said. "Computer technicians at most offices couldn't do anything but sit by helplessly as people worked through stacks of filing, wrote business-related letters they'd put off for months, and sold record amounts of goods and services over the phone."
BOSTON—An Internet worm that disabled networks across the U.S. Monday and Tuesday temporarily thrust the nation into its most severe maelstrom of productivity since 1992.
"In all my years, I've never seen anything like this," said Price Stern Sloan system administrator Andrew Walton, whose effort to restore web service to his company's network was repeatedly hampered by employees busily working at their computers. "The local-access network is functioning, so people can transfer work projects to one another, but there's no e-mail, no eBay, no flaminglips.com. It's pretty much every office worker's worst nightmare."
According to Samuel Kessler, senior director at Symantec, which makes the popular Norton Antivirus software, the Internet "basically collapsed" Monday at 8:34 a.m. EST.
The Gibe-F worm, an e-mail-transmittable virus, initiated cascading server failures. Within an hour, Internet service to more than 90 percent of the U.S. was disabled, either by the worm or by network firewalls that initiated security protocols.
"Unlike SoBig or Blaster, this worm didn't harm individual computers; it just used them as a gate to attack the Internet at the ISP level," Kessler said. "Computer technicians at most offices couldn't do anything but sit by helplessly as people worked through stacks of filing, wrote business-related letters they'd put off for months, and sold record amounts of goods and services over the phone."
Wednesday, May 17, 2006
BackTrack Live CD: Pre-Release Beta Preview
This past weekend, I was given access to the latest BackTrack Live beta. This is a pre-release legal leak, so don't worry about that part =)
After booting up and looking over the tools quickly, here is what I have.
Kernel – Linux Slax 2.6.15.6
Firefox – 1.5.0.3
Nmap – 4.03
KDE – 3.5.0

There were several tools that were not totally up-to-date, like Ethereal, but I assume there will be another tool update before the finally release. It looks like they were right in the middle of a tool upgrade, I saw several version of John the Ripper and a couple of other tools. I did notice the new Metasploit 3 Alpaha in there as well. ;)


All the normal tools are included. Anyone that has used Backtrack before knows the list is huge, so I won’t even attempt to do that, but if you haven’t see the list – check it.

The new wireless driver switcher is pretty cool as well.
Nice work to the Remote-exploit.org team and all the testers.
I have to run back to work, but look for the new release really really soon.
After booting up and looking over the tools quickly, here is what I have.
Kernel – Linux Slax 2.6.15.6
Firefox – 1.5.0.3
Nmap – 4.03
KDE – 3.5.0
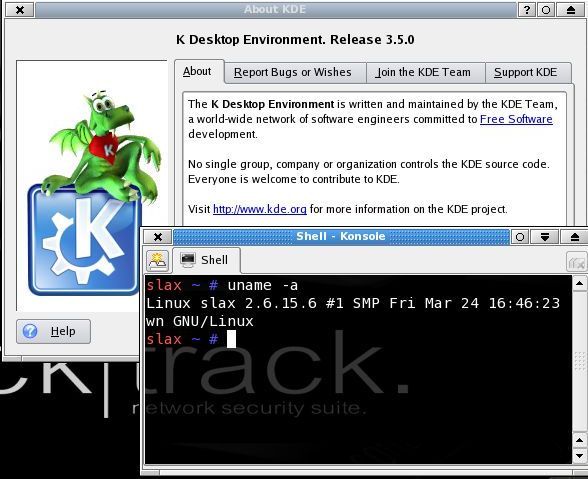
There were several tools that were not totally up-to-date, like Ethereal, but I assume there will be another tool update before the finally release. It looks like they were right in the middle of a tool upgrade, I saw several version of John the Ripper and a couple of other tools. I did notice the new Metasploit 3 Alpaha in there as well. ;)
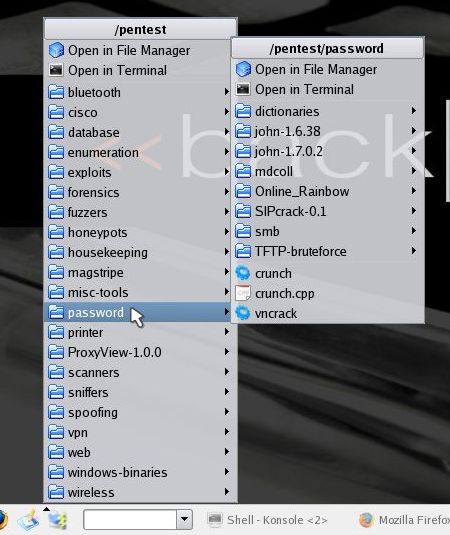

All the normal tools are included. Anyone that has used Backtrack before knows the list is huge, so I won’t even attempt to do that, but if you haven’t see the list – check it.
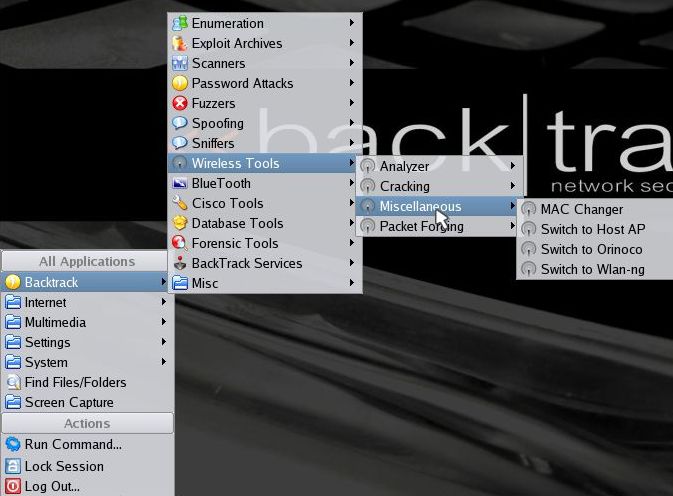
The new wireless driver switcher is pretty cool as well.
Nice work to the Remote-exploit.org team and all the testers.
I have to run back to work, but look for the new release really really soon.
Subscribe to:
Posts (Atom)