Via Thepiratebay.org -
In the morning of 2006-05-31 the Swedish National Criminal Police showed a search warrant to RixPort80 personnell. The warrant was valid for all datacentres of RixPort80 and was directed at The Pirate Bay. The allegation was breach of copy-right law, alternatively assisting breach of copy-right law.
I suppose it was only a matter of time.....
Wednesday, May 31, 2006


Stardust: OpenOffice PoC Virus
A new PoC virus has been developed that targets OpenOffice and StarOffice only.
Check this SF article for more details.
An unknown virus writer has created the first macro virus that targets computers running the alternative word processors OpenOffice and StarOffice, antivirus firm Kaspersky Labs said on Tuesday.
The virus, which Kaspersky called StarOffice.Stardust.A on its Viruslist blog, is written in StarBasic, a variant of the BASIC programming language designed for scripting common functions in the StarOffice and OpenOffice word processors. While the virus attempts to spread to computers through OpenOffice and StarOffice, Kaspersky called the functionality theoretical.
Tuesday, May 30, 2006
Fun: Recently Unearthed E-Mail Reveals What Life Was Like In 1995
It was on theOnion.com, it has to be true.
Sunday, May 28, 2006
THC Courts Phone Hackers
On May 25th, The Hackers Choice (THC) released ROMs and memory mapping information for a nice group of Nokia mobile phones.
Posted on THC.org by DerSteppenwolf :
THC is the world's first group to release ROM images and memory maps from Nokia Mobile Phones. This is an invitation for Reverse Engineers and hackers to discover hidden secrets and backdoors on mobile phones.
http://thc.org/thc-rom/
Posted on THC.org by DerSteppenwolf :
THC is the world's first group to release ROM images and memory maps from Nokia Mobile Phones. This is an invitation for Reverse Engineers and hackers to discover hidden secrets and backdoors on mobile phones.
http://thc.org/thc-rom/
The Perfect Recipe for Defacement
It is that time of year. College is ending and summer is about to begin - the perfect recipe for defacement.
It appears that Turkey as a whole isn't letting up on the defacements. They can account for over half of all the defacements tracked by Zone-H.org - taking the spot from Brazil just recently.
Recent Turkish Defacements
aLpTurkTegin - http://woodlandsperfumers.com/
SanalYargic - http://grupocastor.com.uy/portal/index.php
TurkStorm.Org - http://www.progtv.be/
yusufislam - http://gladtidingsofduluth.org/forum/
narcotic - http://upload.neuper-team.com/index.html
The list goes on and on....
The Internet Storm Center is already reporting a possible "script kiddie contest" underway. Crazy kids.
Looks like alot of the defacements are caused by PHP security issues.
Saturday, May 27, 2006
BackTrack 1.0 Final Released
Remote-exploit.org has finally released BackTrack 1.0 Final.
If you are still using Security Auditor or WHAX, then catch up with the times and get the new BackTrack...you will be glad you did.
If you are still using Security Auditor or WHAX, then catch up with the times and get the new BackTrack...you will be glad you did.
Apple Failed in Battle to Slient the "Media"
Charles Cooper has a great article over at CNet.com -
Hopefully Apple is making an effort to find the leaks inside, instead of just pulling the A-team of lawyers out at the drop of a hat.
Friday, May 26, 2006
Microsoft Word Unspecified Remote Code Execution - UPDATED
I am a little late on this update, but I have been really busy this week. The exploit is a zero-day for sure.
Most of the antispyware friends that I talked to have samples and didn't really see anything different than has already been reported. But it did take a while for everyone to get a sample, this shows just how rare it is in the wild.
I have a sample as well, but haven't had a chance to look at it. I have almost zero RCE skills, so I don't think having a sample is going to help me understand it much better.
The first attack was very limited in scope and Microsoft appears to be doing the right think and will not jump the gun to release a patch early. Some people are giving them hell about that, but I don't see a real reason for them to rush it at this point - in this exact case.
In some cases, it doesn't make sense to hold the patch until Patch Tuesday.
If the vulnerable function is known and being exploited in the public, then the patch should be released as soon as it is ready. Releasing it early in this current case, will expose the true vulnerability to groups that may not have it now, and in the end this will only increase the number of active exploits against this vector.
SANS - http://isc.sans.org/diary.php?storyid=1345
Microsoft - http://www.microsoft.com/technet/security/advisory/919637.mspx
Blah: Long Weekend
Well, I am on my way back from Washington DC. Been a crazy long week, I am ready to get home.
It is amazing the see how empty the Houston airport can be on a Friday night. All the shops are closed and my ice latte is all watered down now. I suppose it is time to break out the redbull and security books until my flight.
Everyone have a great holiday weekend and don't get into too much trouble.
For your weekend reading, check up on the new Norton Corporate Anti-virus hole discovered by eEye and read about this special ring-tone used by teenagers in class.
Wednesday, May 24, 2006
ScanDoo Beta - Making Searching Safe
I just found this pretty cool search engine today. It doesn't replace Google, it just makes it more safe for the public.
It is called ScanDoo.
Scandoo is based on ScanSafe’s web security technology that currently scans billions of web requests for corporate employees around the world. ScanSafe software developers were often asked by their friends and family if they could protect home Internet use in the same way that they protect corporate users. When our lab came up with safe searching technology we thought it was such a good idea that we wanted to make it available to all.
When you search in Scandoo, each site is compared to the ScanSafe's database and given an icon.
This is a great idea for those people that search at work...and don't want the proxy admin at their desk ;)
It is called ScanDoo.
Scandoo is based on ScanSafe’s web security technology that currently scans billions of web requests for corporate employees around the world. ScanSafe software developers were often asked by their friends and family if they could protect home Internet use in the same way that they protect corporate users. When our lab came up with safe searching technology we thought it was such a good idea that we wanted to make it available to all.
When you search in Scandoo, each site is compared to the ScanSafe's database and given an icon.
- Green Check is safe
- Yellow is a warning
- Red is bad
- Black Bug is totally unsafe - known website that contains malware or evil script
This is a great idea for those people that search at work...and don't want the proxy admin at their desk ;)
Tuesday, May 23, 2006
Veterans Affairs Department- data on millions of veterans stolen
Via GCN.com -
The Veterans Affairs Department today revealed that personal, identifying data for as many as 26 million American veterans was stolen from a VA employee's home in May. The information is a list of all veterans who served in the military and were discharged since 1975. A VA employee took files home as part of department work on a data collation project to simplify some VA processes. Subsequently, someone broke into the employee’s home and stole the data. The career employee, a data analyst, was not authorized to take the files home, said VA secretary Jim Nicholson in a teleconference with reporters. He would not say what form the data was in.
I am going to guess and say CSV. ;)
In light of this news, William Jackson wrote a pretty good little article over at GCN.com as well. It is just a reminder that we aren't just holding a PC in our hands, we are holding data that other people might want.
Sunday, May 21, 2006
Google Summer of Code 2006
It is almost that time again. On Tuesday (May 23th), the official projects will be released on the Google Summer of Code website.
While it is impossible to talk about all the possible projects, here are a couple of ideas from a couple of the project. Remember, these are just ideas. Students are welcome to submit original ideas and we will see some of those when the dust settles.
Apache SoC 2006
Mozilla SoC 2006
FreeBSD SoC 2006
My coding skillz are very very far from Kung Foo level, but I just might apply for this project idea suggested for Nmap SoC 2006:
------------------------
Slacker
Nmap developers are known as some of the most productive in the open source world. In order to crank out more code, many eschew luxuries like classes, social lives, sex, and sleep. To counterbalance all of this planned productivity, we may need some experienced slackers to spend the summer playing video games, watching TV, reading Slashdot, and dating. You will report these activities in a weekly status report so the rest of us can live our lives vicariously through yours.
Since lazyness is a virtue for this position, our normal application form is not required. Just tell us your best time-wasting story or any other relevant credentials for this critical role.
------------------------
In 2005, there were around 43 mentoring groups signed up for the Summer of Code.
This year they have over 100.
This fall, we should see a ton of great enchancements and new features created by the community for the community. Open source, it is a good thing....
Saturday, May 20, 2006
New Computer Laws - Are they too Broad?
Recently, several new bills here in the US and in the EU could have a pretty big impact on the IT security world. Are they too broad? Can we fix them before it is too late? Is it even possible to fix them?
There are hard questions and I don't have all the answer, but here are same of my thoughts on the issue.
There are hard questions and I don't have all the answer, but here are same of my thoughts on the issue.
1) Dual-Edged Sword - The tricks, skills and tools of the IT security world are commonly called dual-edged swords. Security tools are just that - tools, no different than a gun, a sword, a hammer or a butter knife. We deal with these pretty good in the real world. Cops don't go out into the woods and arrest hunters because they are carrying shotguns. Do they? Intent and context are the true factors that give the law weight. Exploits, like guns, can be used to break into a network...but that same exploit can be used by a security network admin to find a vulnerable server on the network and as a result jump start the protection process.
2) The Grey World - For a long time, I have talked with my friends about the balance of the force in the world. People have the ability to be good or bad, tools have the ability to be used for good or bad. The world truly is Yin and Yang. I am a huge believer in maintaining the balance. Most of the governments in the world are based on the idea and will fail to function without it. If the balance is not maintained, then things start to function in ways that are not desired - Absolute power corrupts absolutely.
So how do we as a world, apply the black & white letters of the law to a world of grey? Very carefully, that is how. It is like a never ending dance...ever changing, ever shaping. What is illegal today could be legal tomorrow...and vice vera. This idea seems very simple when applied to the real world...but it becomes much more cloudy when applied to the virtual world.
We are seeing just how cloudly with these new bills:
1) Possible Update to the UK Computer Misuse Act (CMA)
2) Truth in Caller ID Act of 2006 - this one is pretty good since this trick rarely needed beyond law enforcement....that assumes I am ok with PI's tricking people..umm...I guess so.
4) UK RIP Act - forcing people to hang over encryption keys....
So how do we make objective laws that take into account subjective intent and context? That is a question for the ages, I think.
Friday, May 19, 2006
Microsoft Word Unspecified Remote Code Execution
Several anti-virus companies have identified a new unspecified attack against Microsoft Word. It is currently being to drop a backdoor trojan onto the target. Once infected the computer attempts to connect to a server in China (localhost.3322.org).
Symantec has tagged the new backdoor as Backdoor.Ginwui. Norton detects the dropped trojan as Trojan.Mdropper.H - but this is expected to change in my view. This dropped trojan could be replaced in the future with a new altered trojan that is not detected.
Some people are using the term 0-day, but until more information is known, I don't want to use that.
Remember that Microsoft patched several Office remote code execution bugs in MS06-012.
Thursday, May 18, 2006
Fun: 48-Hour Internet Outage Plunges Nation Into Productivity
Via TheOnion.com -
BOSTON—An Internet worm that disabled networks across the U.S. Monday and Tuesday temporarily thrust the nation into its most severe maelstrom of productivity since 1992.
"In all my years, I've never seen anything like this," said Price Stern Sloan system administrator Andrew Walton, whose effort to restore web service to his company's network was repeatedly hampered by employees busily working at their computers. "The local-access network is functioning, so people can transfer work projects to one another, but there's no e-mail, no eBay, no flaminglips.com. It's pretty much every office worker's worst nightmare."
According to Samuel Kessler, senior director at Symantec, which makes the popular Norton Antivirus software, the Internet "basically collapsed" Monday at 8:34 a.m. EST.
The Gibe-F worm, an e-mail-transmittable virus, initiated cascading server failures. Within an hour, Internet service to more than 90 percent of the U.S. was disabled, either by the worm or by network firewalls that initiated security protocols.
"Unlike SoBig or Blaster, this worm didn't harm individual computers; it just used them as a gate to attack the Internet at the ISP level," Kessler said. "Computer technicians at most offices couldn't do anything but sit by helplessly as people worked through stacks of filing, wrote business-related letters they'd put off for months, and sold record amounts of goods and services over the phone."
Wednesday, May 17, 2006
BackTrack Live CD: Pre-Release Beta Preview
This past weekend, I was given access to the latest BackTrack Live beta. This is a pre-release legal leak, so don't worry about that part =)
After booting up and looking over the tools quickly, here is what I have.
Kernel – Linux Slax 2.6.15.6
Firefox – 1.5.0.3
Nmap – 4.03
KDE – 3.5.0

There were several tools that were not totally up-to-date, like Ethereal, but I assume there will be another tool update before the finally release. It looks like they were right in the middle of a tool upgrade, I saw several version of John the Ripper and a couple of other tools. I did notice the new Metasploit 3 Alpaha in there as well. ;)


All the normal tools are included. Anyone that has used Backtrack before knows the list is huge, so I won’t even attempt to do that, but if you haven’t see the list – check it.

The new wireless driver switcher is pretty cool as well.
Nice work to the Remote-exploit.org team and all the testers.
I have to run back to work, but look for the new release really really soon.
After booting up and looking over the tools quickly, here is what I have.
Kernel – Linux Slax 2.6.15.6
Firefox – 1.5.0.3
Nmap – 4.03
KDE – 3.5.0
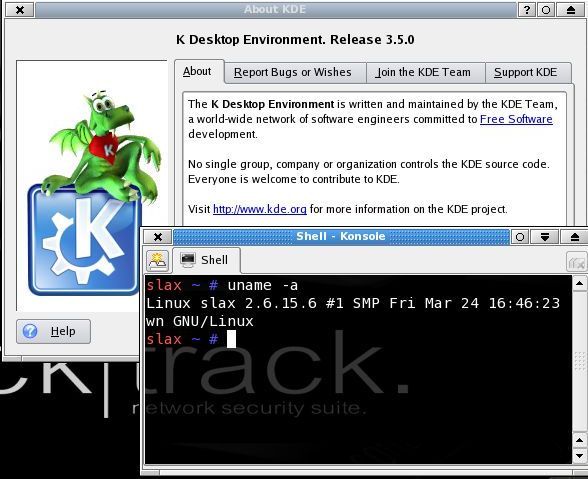
There were several tools that were not totally up-to-date, like Ethereal, but I assume there will be another tool update before the finally release. It looks like they were right in the middle of a tool upgrade, I saw several version of John the Ripper and a couple of other tools. I did notice the new Metasploit 3 Alpaha in there as well. ;)
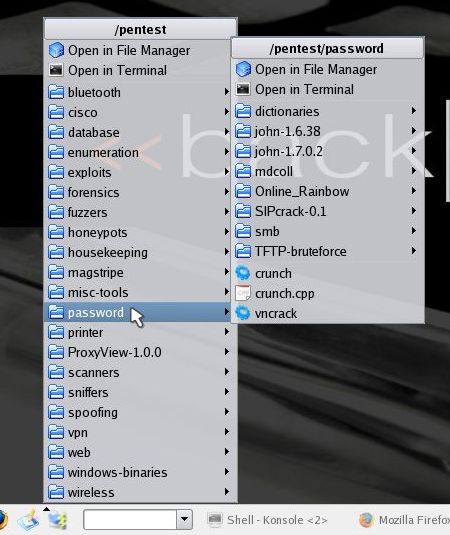

All the normal tools are included. Anyone that has used Backtrack before knows the list is huge, so I won’t even attempt to do that, but if you haven’t see the list – check it.
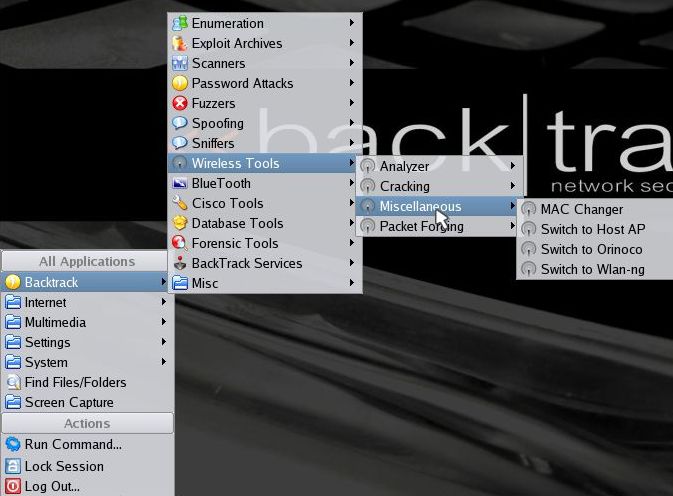
The new wireless driver switcher is pretty cool as well.
Nice work to the Remote-exploit.org team and all the testers.
I have to run back to work, but look for the new release really really soon.
Apple Releases a Whopping 43 Security Updates
Via DailyTech.com
Apple last week released a massive security update package for their Mac OS X operating system as well as updates for the QuickTime player bundled with Mac OS X. The update fixes a number of security issues including a number of code execution vulnerabilities that could allow an attacker to compromise Mac OS X and run undesirable programs.
The update also includes fixes for Apples popular Quick Time player that could allow an attacker to use malformed media files launch denial of service attacks or compromise a users system. The update to QuickTime also improves the applications stability.
The Mac OS X update also fixes code execution vulnerabilities in AppKit, ImageIO, BOM, CFNetwork, ClamAV, CoreFoundation, Finder, FTPServer, FlashPlayer, LaunchServices, libcurl, Preview, QuickDraw and QuickTime Streaming Server.
Anyone have a breakdown on the time between fixes in the open source world and when they are fixed in OS X??
ClamAV and several of the other products are open source, and it is well known that vulnerabilities found in open source products are also found in their OS X couterparts.
This fact isn't something that Apple can afford to overlook. When open source products are patched, the details are handed to the bad guys. How long will that vulnerability exist in OS X before it is fixed??
When Spammers Hit Back
Wired.com has a great article on the work conducted by Blue Security. However, Blue Security has put down its weapon and left the ring. But those guys can remember that they did make a difference and presented an outside-the-box method of fighting spam.
Perhaps one day, the Can-Spam Act can be used to fight the real spam problem, at this point it is just a sheet of paper in my view. Used against real companies that make mistakes, it isn't stopping PharmaMaster and others like him.
------------------------------
Starting May 2, a spammer known as PharmaMaster used a massive network of zombie computers to flood Blue Security's database servers with fake traffic and hijacked a little-known Cisco Systems router feature known as "blackhole filtering" to block anyone outside Israel from accessing Blue Security's homepage.
Blogging software provider Movable Type's hosted service, TypePad, also fell victim to PharmaMaster's bot network, after Blue Security realized that no one could reach its homepage and posted a message to its users on its old blog. Thirty minutes later, PharmaMaster started an attack that brought down thousands of blogs.
Tuesday, May 16, 2006
Myspace Phishing Attacks on the Rise
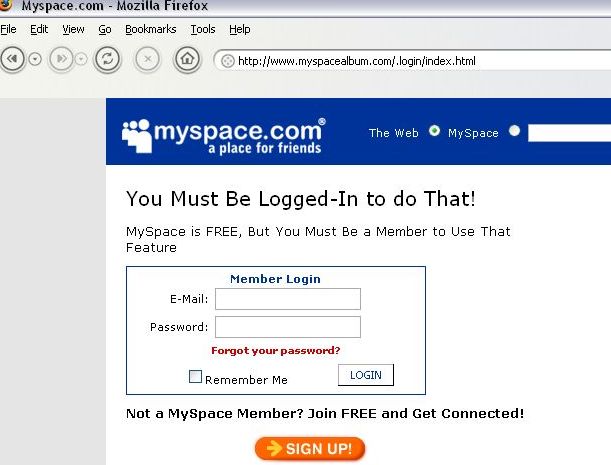
Phishing Attacks against the very popular social networking website are on the rise.
Newest one discovered - http://www[dot]myspacealbum[dot]com/.login/index.html
Abuse Contact @ the Domain has been alerted by e-mail.
This URL was passed around in a bulletin titled "CHECK OUT these old school pictures...". The bulletin was posted by a friend without his knowledge.

Malware or some type of script injection attack might be the bulletin posting vector.
But if they can send bulletins as you without your knowledge, then can install a bank info stealing trojan with a IE vulnerability. The malware or attack script could alter your profile enough that all visitors (your friends) get attacked via drive-by-install.
Within the past week, another bulletin about "party pictures" was used to spread another phishing URL.
Perhaps Myspace should use some of those ad dollars and think about getting a security@myspace email account working ;)
The collected e-mails and passwords could be used to collect more important information. Tons of people use the same password for both for multiple pages.
Lets just hope that most of the younger people don't have paypal accounts ;)
As these social network groups grow, they are now in the crosshairs to become a future attack vector.
Malware distributors can operate hidden behind the cloak of "fun harmless social interaction" and take advantage of client-side vulnerabilities via script injection - Myspace worm ring a bell.
Sun to Open Source Java
Via ComputerWorld -
SAN FRANCISCO -- Sun Microsystems Inc. at its JavaOne conference today announced plans to open source Java, but said before it does so company officials have to be certain the move won't lead to diverging paths in the code.
Very interesting but not totally shocking. Sun already has plans to move Solaris totally into the open source model. OpenSolaris.org was opened and already has working open source OS.
In the end, it will be kinda like the Fedora project before the Fedora Foundation was created =)
Perhaps Sun sees that the open source model is the only way to stay in the fight ;)
SAN FRANCISCO -- Sun Microsystems Inc. at its JavaOne conference today announced plans to open source Java, but said before it does so company officials have to be certain the move won't lead to diverging paths in the code.
Richard Green, Sun's executive vice president of software, made it absolutely clear that Java would be opened source.
Very interesting but not totally shocking. Sun already has plans to move Solaris totally into the open source model. OpenSolaris.org was opened and already has working open source OS.
In the end, it will be kinda like the Fedora project before the Fedora Foundation was created =)
Perhaps Sun sees that the open source model is the only way to stay in the fight ;)
Subscribe to:
Posts (Atom)